Required for core functionality such as security, network management, and accessibility. These cannot be disabled.
Top Generative AI Company
Award by Clutch for the Top Generative AI Company
Whether in finance, healthcare, or tech, our DevSecOps services are customized to meet
your specific security needs and challenges.
At TechAhead, we offer a holistic DevSecOps approach that seamlessly integrates security into your development and operations processes. Our services encompass everything from initial threat modeling and risk assessment to automated security testing and continuous monitoring.
Partner with the enterprise DevOps team to gain valuable insights into your DevSecOps strategy. Integrate high-end security measures to identify vulnerabilities early and proactively resolve them.
Bring consistency and standardization to your security practices across all environments and deployments with DevSecOps security automation solutions. This reduces the risk of oversight and increases the overall security posture of your software.
Develop reliable software products by proactively addressing security concerns throughout the development lifecycle. Minimize the risk of data breaches, protect user privacy, and maintain the integrity of your applications.
DevSecOps experts are proficient in SAST, which catches critical security flaws such as SQL injection and buffer overflow. This significantly reduces the risk of potential vulnerabilities and leads to cleaner, more maintainable code.
The DevSecOps maturity model includes DAST, which actively interacts with software functionality to help you uncover every possible issue that could compromise the confidentiality, integrity, or availability of critical business processes and data.
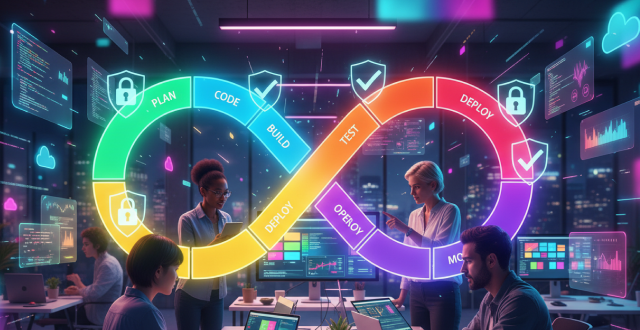
From vulnerability scanning and code analysis to automated security testing and compliance checks, DevSecOps CI/CD pipelines create a proactive security framework that actively prevents and detects vulnerabilities before they can wreak havoc.
Our DevSecOps services integrate security throughout your development lifecycle, accelerating delivery while maintaining enterprise-grade protection. Automated security frameworks reduce vulnerabilities and compliance risks across your software infrastructure.
Turn Your Idea Into an AI Smart Mobile Product.
Connect with Our Experts Today to Architect a Next-Generation App Strategy.
Empowering Global Brands and Startups to Drive Innovation and Success with our Expertise and Commitment to Excellence
Read TechAhead's real-world examples that show how DevSecOps empowers both profitable and
non-profitable industries with custom apps for better outcomes and efficiency.
The challenges in developing the Relationship Card Game App included designing engaging gameplay mechanics, ensuring a smooth user experience, integrating interactive features, and maintaining scalability across platforms.
We developed a cross-platform Flutter app, which allows ultra-low latency video calling powered by Agora.io and Python, seamlessly integrated with a scalable AWS architecture. Following DevSecOps best practices, the solution supports real-time conversations among thousands of users worldwide.
The existing mobile application suffered from complicated navigation, information overload, poor user experience, decreased engagement, confusing interface layers, and declining user adoption of their heating control system.
Built native mobile apps using Swift (iOS) and Java (Android), supported by Python-based backend APIs. The solution followed a strong DevSecOps foundation for secure delivery. Deployed infrastructure on AWS with RabbitMQ and Redis for real-time messaging. Integrated with popular smart home ecosystems/assistants: Google Home, Apple HomeKit, Alexa, IFTTT.
The main challenge was creating a positive social platform, removing likes and negativity. This platform ensures privacy with face-blur features and designs an engaging, uplifting experience without comparison or social pressure.
Created an app where users upload outfit polls (one or more outfit options), set poll durations, and let the community pick the winning look. Built with a DevSecOps-first approach, it includes strong anonymity and privacy features: users can conceal names, blur faces and backgrounds to share outfits without identifying themselves. Removed stress-inducing social media mechanics: no likes or visible comment counts, no negative feedback display.
Opting for a DevSecOps culture revolutionizes your organization's approach to security in software development. By embedding security practices from the outset, teams can detect and resolve vulnerabilities early, minimizing risks and enhancing compliance with regulatory standards.
The DevSecOps services and solutions bring security to the forefront by implementing security controls, continuous monitoring, and automated security testing. This allows for proactive identification and remediation of vulnerabilities early in the development process.
DevSecOps consulting services help deliver quality code while reducing the risk of vulnerabilities. This ensures faster time-to-market, providing businesses with a competitive edge and the ability to respond swiftly to market demands.
In DevSecOps managed services, quality is not just an isolated phase but a continuous focus throughout development. This leads to higher-quality software that meets customer expectations, resulting in increased customer satisfaction and loyalty.
DevSecOps services help you align with regulatory standards right from the start, reducing the compliance burden and ensuring a smoother path to regulatory approval. This not only helps avoid penalties and reputational damage but also builds trust with customers and stakeholders.
A key pillar of the DevSecOps maturity model is fostering collaboration and breaking down organizational silos. This model also fosters an environment where knowledge-sharing and collective problem-solving can thrive.
We help you embed security into every stage of your software delivery lifecycle through strategic DevSecOps transformation.
Your idea needs a high-quality experience for your users. Here, we help you combine your vision with our technical expertise to build mobile apps that truly make a difference. We make the entire mobile app development process smooth and results-focused.
Our expert software developers, security analysts, and operations engineers create secure DevSecOps pipelines tailored for enterprises.
We build flexible automation frameworks that support rapid scaling, seamless integration of new tools and consistent performance as your infrastructure expands.
We follow continuous security checks, automated vulnerability scanning, and compliance monitoring within your CI/CD pipelines to protect enterprise assets.
Our developers customize tooling and processes based on your unique infrastructure, compliance requirements, and risk profile for secure delivery.
At TechAhead, we build mobile apps that are not only feature-rich and scalable —
they’re built with compliance, security, and regulatory integrity baked in.
At TechAhead, we consistently stay ahead of the competition with our latest tools and technologies for mobile app development. Our commitment to innovation ensures superior services that meet our clients' evolving needs.
We integrate security deeply into your development and operations processes. Our DevSecOps services maintain faster, safer releases through continuous integration and proactive vulnerability management.
We partner with startups, scaleups, and enterprises to design and build AI-native platforms, systems, and applications that operate reliably in the real world.
From taking AI out of pilots and into production, to modernizing core systems that teams depend on every day, our work is measured by long-term outcomes—not just launches. These are the voices of teams who trusted us to build systems that scale, evolve, and deliver real impact.
See how we empower organizations across sectors with customized security strategies that safeguard assets
and support business growth and innovation.
As requirements change or expand, engagement often extends into complementary technology capabilities. Our work reflects this by supporting multiple initiatives across several technology areas—helping organizations modernize, scale, and accelerate delivery with confidence.
Award by Clutch for the Top Generative AI Company
Award by The Manifest for the Most Reviewed Machine Learning Company in Los Angeles
Award by The Manifest for the Most Reviewed Artificial Intelligence Company in Los Angeles
Award by The Manifest for the Most Reviewed Artificial Intelligence Company in India
Award by Clutch for Top App Developers
Award by Clutch for the Top Health & Wellness App Developers
Award by Clutch for the Top Cross-Platform App Developers
Award by Clutch for the Top Consumer App Developers
Honoree for App Features: Experimental & Innovation
Awarded as a Great Place to Work for our thriving culture
Recognised by Red Herring among the Top 100 Companies
Award by Clutch for Top Enterprise App Developers
Award by Clutch for Top React Native Developers
Award by Clutch for Top Flutter Developers
Award by Manifest for the Most Number of Client Reviews
Awarded by Greater Conejo Valley Chamber of Commerce
Schedule a Complimentary Consultation to Discuss
AI Integration and Project Roadmap with Our Tech Leaders.
We run continuous Software Composition Analysis (SCA), generate/maintain SBOMs, and auto-create tickets/PRs for vulnerable packages with version-pinning and policy gates (e.g., block builds on critical CVEs). Vendor feeds (NVD, GitHub Advisories) keep signatures up to date; exceptions require risk sign-off.
Security runs as code in your pipeline: pre-commit hooks (secrets/linters), build-time SAST/DAST/SCA, container image scanning, IaC checks (Terraform/Kubernetes), policy-as-code (OPA), and deployment gates tied to severity thresholds. Works with GitHub Actions, GitLab CI, Azure DevOps, Jenkins, etc.
Shift-left practices reduce mean-time-to-remediate (MTTR), cut critical vulnerabilities reaching prod, and raise coverage. Typical results: 30–50% faster fixes, >90% secrets detection before merge, and zero-touch patching for known CVEs via automated PRs.
Traditional security checks are late and block releases. DevSecOps builds security into daily work: code reviews with security rules, automated scans per commit, policy gates in CI/CD, and runtime guardrails—yielding fewer surprises, faster releases, and lower risk.
Yes. Start lean with managed scanners, pre-built CI templates, and a shared security backlog. We offer tiered packages (Starter, Growth, Enterprise) so smaller teams get essentials—SAST/SCA/secrets/IaC checks and minimal gating—then scale up as needs grow.
We embed compliance checks into pipelines (e.g., CIS Benchmarks, OWASP Top 10) and generate audit-ready reports. Our solution aligns with SOC 2, HIPAA, GDPR, and ISO 27001, providing traceable evidence for every change.
Yes. Every scan, policy decision, and remediation is logged with immutable audit trails. We generate automated compliance dashboards and on-demand exportable reports for auditors.
Yes. We integrate natively with AWS, Azure, and GCP—covering services like IAM, EKS/AKS/GKE, Lambda, and cloud storage. Misconfigurations are flagged in CI/CD before deployment.
Yes. We scan container images for vulnerabilities, enforce signed/verified builds, and run Kubernetes admission controllers with policy-as-code (OPA/Gatekeeper) to block risky deployments.
Yes. Vulnerabilities and misconfigurations auto-create tickets in Jira or ServiceNow with severity, fix guidance, and SLAs—streamlining collaboration between Dev and SecOps teams.
Key KPIs include: Vulnerability MTTR, % vulnerabilities fixed before release, coverage of SAST/DAST/SCA scans, % policy compliance, and number of high-risk issues blocked in the pipeline.
Every finding is tracked with timestamps from detection to fix. Automated PRs, prioritized backlog integration, and severity-based SLAs reduce MTTR by up to 50%.
We continuously ingest threat intel (NVD, CISA KEV, vendor feeds). Zero-days trigger pipeline policy updates, prioritized alerts, and mitigation steps (e.g., temporary blocks, compensating controls) within hours.
Yes. We integrate with runtime security tools (Falco, AWS GuardDuty, Azure Defender) to enable anomaly detection, container drift alerts, and real-time notifications in SIEM/SOAR systems.
We provide lightweight pre-commit checks, developer-friendly IDE plugins, and auto-fix pull requests. This shifts security left without bottlenecks, so developers stay productive while improving security.
Yes. We run hands-on workshops and e-learning for developers, DevOps Engineers, and security teams—covering secure coding, pipeline integration, and incident response.
We offer 24/7 monitoring, incident response, and managed DevSecOps services with defined SLAs. Our team provides patch management, upgrades, and continuous pipeline optimization.
TechAhead's DevSecOps teams operate from California, Noida, and Dubai. We assign work based on your timezone and security requirements. California leads strategy and compliance planning. Noida engineers implement CI/CD pipelines, security automation, and monitoring. Dubai handles Middle East deployments. All locations follow identical security standards, tooling, and quality protocols. Round-the-clock coverage ensures your pipelines stay protected regardless of when code ships.
The overall investment in a business application varies based on technical architecture, functional complexity, integration needs, security compliance, and scalability demands.
Typical investment ranges include:
We collaborate closely with your team to fully understand your business goals and technical needs, enabling transparent pricing and a well-defined delivery plan. Our development approach prioritizes scalability, security, and performance to ensure your application delivers lasting value as your business grows. Feel free to schedule a call to discuss your requirements and define a customized development plan.
We build on zero-trust principles with automated compliance gates for SOC 2, ISO 27001, HIPAA, and GDPR. Every pipeline includes SAST, DAST, SCA scans, secret detection, and container vulnerability checks. Role-based access controls, encrypted secrets management, and audit logs track every change. Infrastructure-as-code validates security policies before deployment. You receive compliance dashboards, automated reports, and evidence packages ready for regulatory audits and penetration testing validation.
We assess your current security posture and define compliance requirements first. Then we architect CI/CD pipelines with integrated security gates, SAST/DAST tools, and secret management. Implementation follows: automated scanning, infrastructure-as-code security, and threat detection workflows Testing validates everything through penetration tests and compliance audits Post-deployment, continuous monitoring tracks vulnerabilities, security metrics, and incident response We also conduct team workshops on secure coding and pipeline management for sustained security practices.
July 21, 2025 | 2257 Views
Chief Commercial & Customer Success Officer
February 14, 2025 | 2063 Views
Sr. Vice President Delivery
February 2, 2024 | 2831 Views
Chief Commercial & Customer Success Officer
We use cookies to enhance your experience, analyze site usage, and support our marketing efforts. You can accept all cookies or manage your preferences.
We use cookies to ensure our website functions properly, improve performance, and provide a personalized experience. You can choose which types of cookies to allow below.
Required for core functionality such as security, network management, and accessibility. These cannot be disabled.
Help us understand site traffic and user interactions so we can improve performance and usability.
Enable enhanced functionality and personalization such as language or region preferences.
Used to deliver relevant ads, track campaign performance, and measure advertising effectiveness.